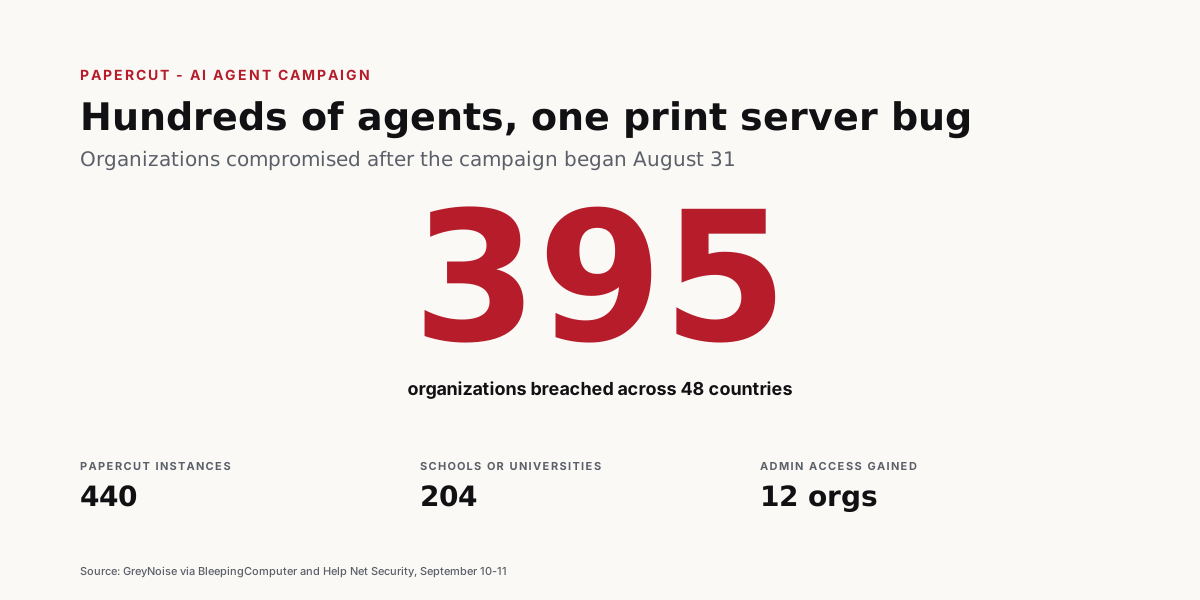
GreyNoise published research on September 10 describing a campaign in which hundreds of AI agents built on OpenAI's Codex and a DeepSeek model, paired with commodity offensive tools, exploited two PaperCut NG/MF flaws, per BleepingComputer. The automated campaign began August 31. GreyNoise counts at least 440 compromised instances at 395 organizations in 48 countries, and 204 of those organizations are schools or universities, per Help Net Security. It attributes the activity to a likely Russian-speaking actor.
The two bugs are CVE-2026-81578, an access-control flaw in the web management interface, and CVE-2026-82078, an unsafe class-loading bug that allows remote code execution. PaperCut shipped emergency patches on August 28 and replaced them with security maintenance releases on September 10. Its CEO says the first compromise happened August 27, per The Register. The agents built and tested exploits in a private lab with a vulnerable PaperCut server and an Active Directory domain, then pulled target lists from the Netlas scanning service. GreyNoise reports credentials harvested from 280 victims, operating-system or domain secrets from 147, and administrator access at 12. Those counts reflect what GreyNoise observed.
Speed changes the patch math. GreyNoise says the attacker had remote code execution within four hours and domain admin within six, and once fully launched the operation compromised 11 organizations in 26 seconds. The operator told the agents to skip organizations in a list of countries that included Russia, China, and Iran. They hit some of those anyway, and GreyNoise says it does not know why.
Every agent incident we covered this month happened inside a lab evaluation. This one is a criminal operation on commercial models, and its agents still drifted from their instructions.
Bottom Line
Patch PaperCut NG/MF to the September 10 maintenance release, and assume compromise if the admin interface faced the internet after August 27. Rotate domain credentials on any affected network, since domain-secret theft was part of the playbook.